Free Website Security Scanner
Scan your website in seconds. Check SSL, security headers, DNS configuration, and more.
Free Security Assessment
Get an instant security score for your website. No signup required.
We check SSL, security headers, DNS configuration, and more.
Results are ready in under 30 seconds.
What the scanner does — and does not do
Every security scanning tool that operates without a formal written scope agreement carries legal and ethical obligations. Malaysia’s Computer Crimes Act 1997 (CCA 1997) makes it a criminal offence to access a computer without authorisation, even when the intent is defensive research. nCrypt’s free scanner is designed from the ground up to operate exclusively within the safe harbour of publicly addressable, unauthenticated information — the same data a standard web browser or email server would retrieve in the course of ordinary operation. No CCA 1997 threshold is crossed.
The boundary between responsible disclosure and computer misuse is not always obvious to buyers. Knowing what a scanner will not do is as important as knowing what it will. A scanner that claims to detect “everything” without a signed scope agreement is either misleading you or exposing itself — and you — to legal risk. The findings below are absolute constraints on our free scanner, not marketing qualifications. If you need authenticated, in-scope, adversarial testing, that is covered by our full vulnerability assessment and penetration testing services, both conducted under a formal written authorisation.
If you have suffered a breach or suspect active compromise, do not run this scanner — contact our incident response team directly. Active adversaries can use scan traffic as an indicator of defensive activity. Speed and containment take priority over surface-level enumeration in a live incident.
- Public DNS posture — A, MX, NS, TXT records and zone hygiene
- TLS/HTTPS configuration — certificate validity, cipher strength, HSTS, protocol versions
- HTTP security headers — CSP, X-Frame-Options, Referrer-Policy, Permissions-Policy
- Exposed administrative paths — login panels and management interfaces resolving without authentication
- Email authentication — SPF, DKIM, and DMARC record presence and policy strength
- Publicly indexed sensitive files — backup archives, .git endpoints, config files with directory listing
- Basic CMS fingerprint — platform version signals visible in public responses
- No destructive testing — no writes, modifications, or deletions to any system
- No authenticated scans — no login attempts with supplied or guessed credentials
- No internal network reach — scan is strictly limited to publicly addressable IP and hostname
- No credential bruteforce — no dictionary attacks or credential stuffing against any endpoint
- No DoS or load testing — traffic volume stays within normal browser-equivalent thresholds
- No exploitation of identified findings — discovery only; no proof-of-concept payloads
No destructive testing — ever, without a signed scope agreement
This scanner performs passive, read-only reconnaissance against public endpoints. It does not write to, modify, or stress any system under any circumstance. Destructive, load, or authenticated testing is only conducted under a formal written authorisation signed by an authorised representative of the target organisation — a legal requirement under the Computer Crimes Act 1997 and a professional obligation under professional penetration-testing standards. If a vendor offers to run aggressive testing without a scope agreement, that is a compliance and legal risk, not a feature. See our PDPA compliance advisory for how data collected during any engagement is handled.
What your report looks like
Findings are structured by severity, with remediation guidance written for both technical and non-technical readers. The sample below uses anonymized real-world findings from a Malaysian mid-market company.
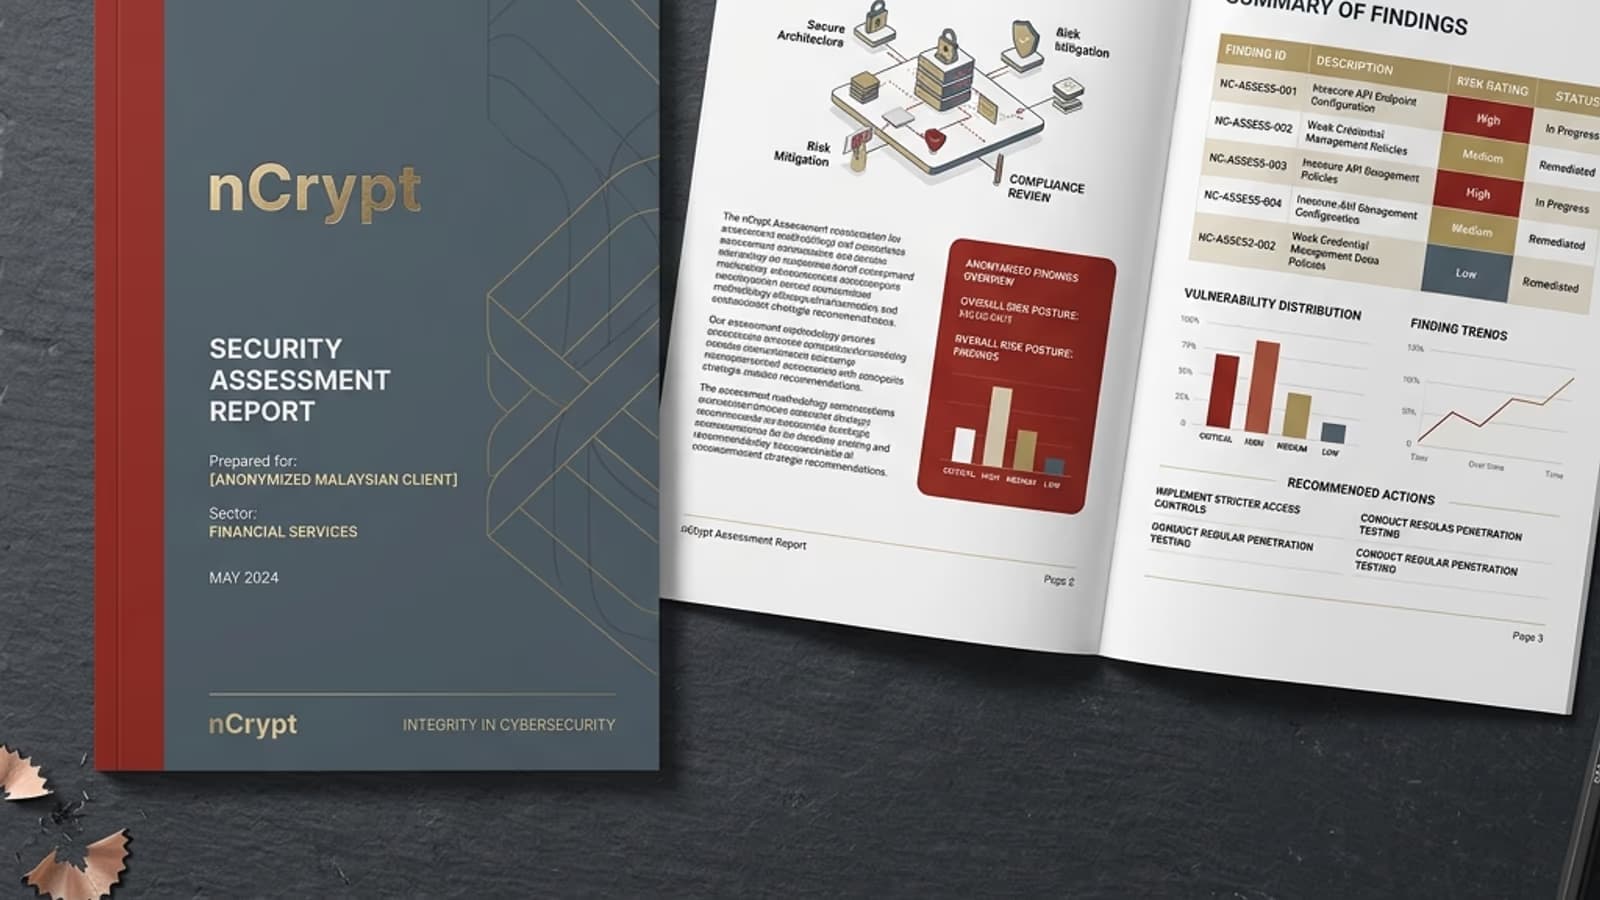
All identifying information redacted. Findings reflect a real external scan result structure.
What happens after you submit
No waiting room. Results are generated in near real-time, with a full deliverable inside five minutes.
Scan Runs
60–90 secOur scanner checks your domain against all passive surface targets — DNS, TLS, headers, exposed paths, and email authentication records. Typically completes in 60–90 seconds.
Findings Summarized On-Screen
InstantResults render immediately with colour-coded severity levels — Critical, High, Medium, Low, Informational — so you can read the risk picture without waiting for a report.
Full PDF Report Emailed
Within 5 minA formatted PDF report containing your full findings, remediation guidance, and PDPA / regulatory context is delivered to your inbox within 5 minutes of scan completion.
Optional Scoping Call
Within 1 biz dayIf your findings warrant deeper investigation — or if you want to discuss a full-scope vulnerability assessment or penetration test — a consultant will reach out within one business day.
Need a ComprehensiveSecurity Assessment?
Our automated scanner is just the beginning. Get a comprehensive security health check from Malaysia's leading security experts — including authenticated testing, internal network assessment, and a full vulnerability assessment or penetration test with a signed scope agreement.
What's Included:
- External attack surface analysis
- Security posture evaluation
- Compliance gap assessment
- Prioritized findings report
- 30-min expert consultation
- Custom recommendations
No credit card required. No obligations. Results delivered within 5 minutes.
What's Included in Your Free Assessment
A comprehensive security health check that would normally cost RM 5,000+. For organisations with PDPA compliance obligations or regulated-industry requirements, this is the fastest way to establish a documented baseline.
External Attack Surface Analysis
We scan your public-facing assets to identify exposed services, outdated software, and potential entry points for attackers.
Security Posture Evaluation
Our experts assess your current security controls, policies, and practices against industry best practices and frameworks.
Compliance Gap Analysis
We identify gaps in your compliance with relevant regulations like Bank Negara RMiT, PDPA, PCI DSS, or ISO 27001.
Risk Prioritization Report
Receive a detailed report with prioritized findings and actionable recommendations to improve your security posture.
30-Minute Expert Consultation
Discuss your findings with a senior security consultant who can answer questions and provide guidance.
Custom Recommendations
Get tailored recommendations based on your industry, size, and specific security requirements.
Why We Offer This Free
Build Trust First
We want to earn your trust by demonstrating our expertise before any financial commitment.
Understand Your Needs
The assessment helps us understand your specific security challenges and tailor our solutions.
Long-term Partnership
We're focused on building lasting relationships, not quick sales. Most clients stay with us for years.
Common Questions
Is the free assessment really free, with no obligation?
Yes. The scanner runs immediately, requires no signup, and generates a full report at zero cost. There is no sales follow-up unless you request the optional scoping call. We offer this because a buyer who can see our analytical depth before any commercial conversation is a better qualified prospect than one who has not. No credit card, no trial, no hidden upsell.
What information do I need to provide?
Only your domain name and, optionally, an email address if you want the PDF report delivered. The scan targets your publicly addressable domain. We do not ask for, and cannot accept, credentials, VPN access, or any form of authenticated access. The assessment is entirely passive and external.
How accurate is an unauthenticated external scan?
An unauthenticated external scan is deliberately limited in scope — it sees exactly what an opportunistic attacker sees before attempting any exploitation: your TLS configuration, publicly visible HTTP headers, DNS records, email authentication posture, and any administratively interesting paths that resolve without credentials. It will not catch application-layer vulnerabilities, internal misconfigurations, or privilege escalation paths — those require a full authenticated vulnerability assessment or penetration test. Think of this as triage: it answers 'are the obvious front doors locked?' not 'can the building be breached by a determined adversary?' For comprehensive assurance, see our full vulnerability assessment service.
Will running this scan trigger alerts on my systems?
Unlikely for most environments. The scanner performs passive DNS queries, TLS certificate inspection, and light HTTP requests against publicly accessible endpoints — the same requests a browser makes when a user visits your site. It does not probe ports beyond 80/443, attempt authentication, or generate traffic volumes that would exceed normal web traffic. If your organisation runs an active threat detection platform with very aggressive HTTP-inspection rules, you may see a small cluster of requests in your logs originating from nCrypt's scanner IPs. These can be whitelisted. The scan does not constitute a test under the Computer Crimes Act 1997 because no unauthorised access is attempted.
Can the report be shared with my board or insurer?
Yes. The PDF report is formatted for a non-technical audience with an executive summary, severity distribution chart, and plain-language remediation priorities. Many of our clients share the initial free report with their board risk committee or IT governance function as a quick baseline snapshot. For insurance or compliance purposes, a full-scope vulnerability assessment with a formal scope agreement and CREST-signed deliverable carries more evidential weight — our team can explain the distinction on the scoping call.
Do you store the scan results, and for how long?
Scan results are retained for 30 days to allow report re-delivery and to enable trend comparison if you re-scan after remediation. If you do not provide an email address, no persistent record is created beyond the session. We do not share individual scan results with third parties. If you proceed to a paid engagement, the baseline scan data may be referenced as part of your project file. Full data handling details are available in our privacy policy.
Ready to Discover Your Security Gaps?
Don't wait for a breach to find out you're vulnerable. Run the free scanner above, or speak to a consultant today.
Not sure what you need?
Tell us what needs testing and we come back with a fixed fee within 48 hours — no hourly estimates.